SECURITY RESEARCH / RESPONSIBLE DISCLOSURE

Bug Bounty

Findings, review histories, and recognition.

A collection of redacted award notifications and security report records, with public write-ups grounded in the accompanying screenshot evidence.

01 / AWARD NOTIFICATIONREDACTED DUE TO NDA

Confidential report · $20,000 award

$20,000 awarded

A redacted HackerOne notification documenting a $20,000 bounty award. Vulnerability details remain withheld.

Read write-up & view evidence

Public record

The supplied notification states that a program rewarded the report with a $20,000 bounty. This write-up preserves that award acknowledgment while withholding the program, report title, affected assets, and technical weakness information.

Disclosure boundary

The notification distinguishes disclosure of the bounty amount from disclosure of weakness information. Accordingly, this public entry contains no vulnerability classification, affected feature, reproduction steps, payloads, or impact details. Those sections are redacted due to NDA.

What the evidence establishes

The screenshot documents an award notification. It is not a bank receipt, a remediation report, or evidence of the date a fix reached production. No additional payout status or remediation claim is inferred.

Outcome and evidence handling

The public outcome is the documented award. Additional opaque redactions were applied to the exported screenshot, and image metadata was removed. The original correspondence is not hosted on this website.

Screenshot evidence
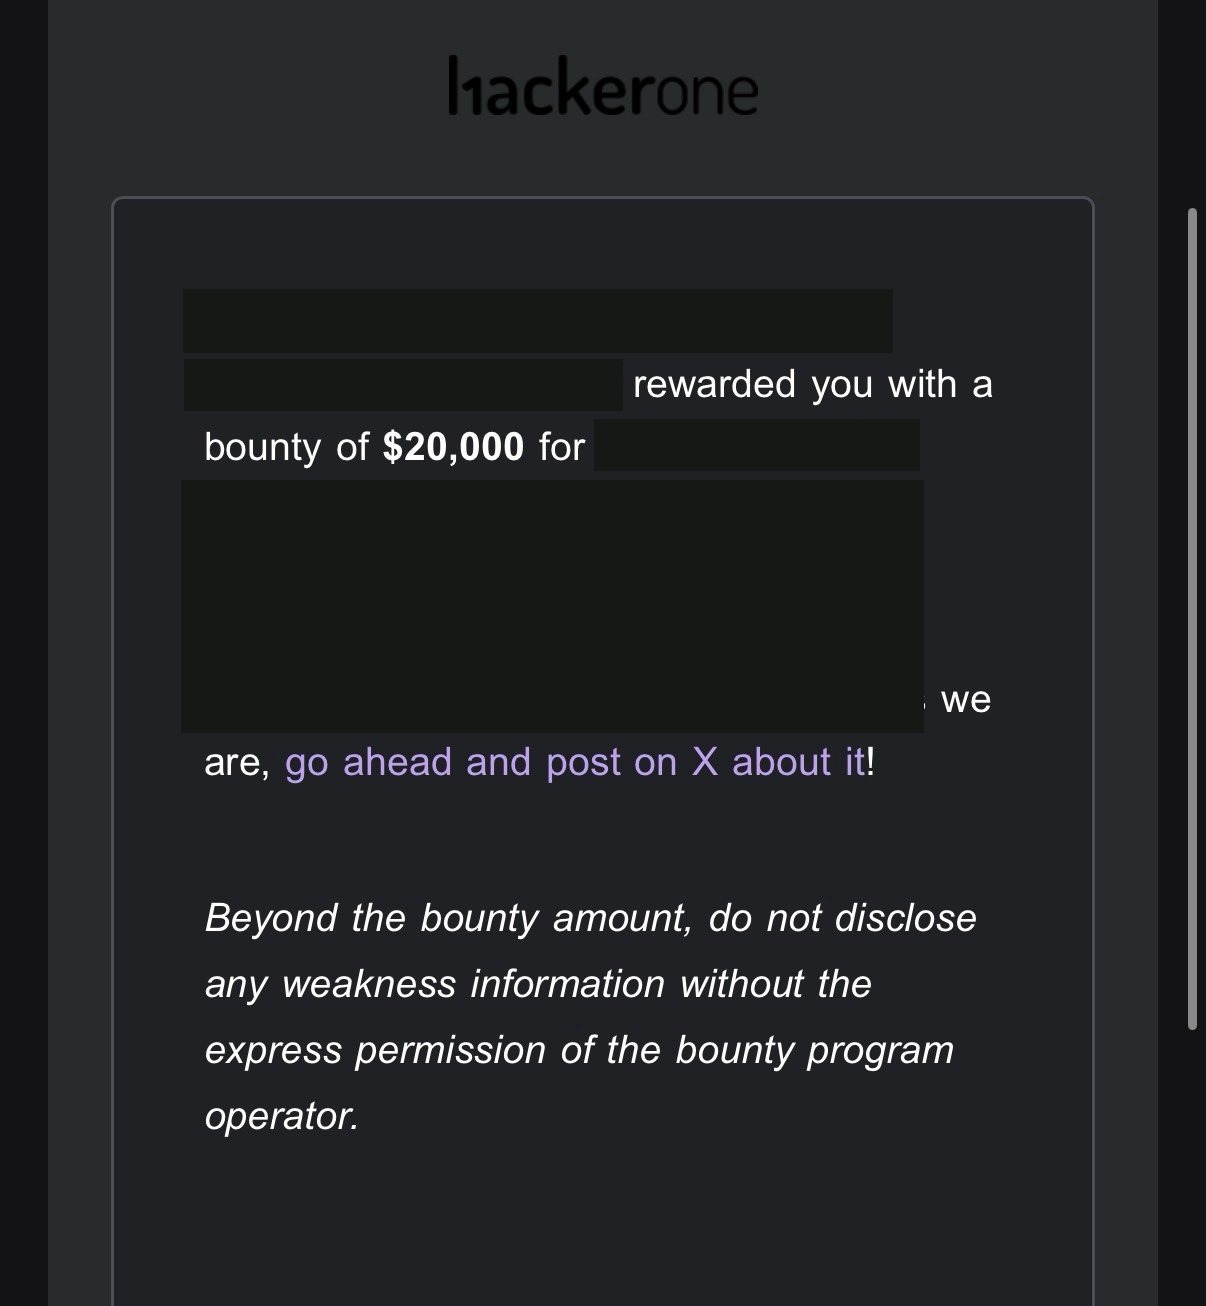
Award notification showing $20,000. Program identity and weakness information are permanently obscured.
Award notification showing $20,000. Program identity and weakness information are permanently obscured. Open full image ↗
02 / AWARD NOTIFICATIONREDACTED DUE TO NDA

Zero-click report · $10,000 award

$10,000 awarded

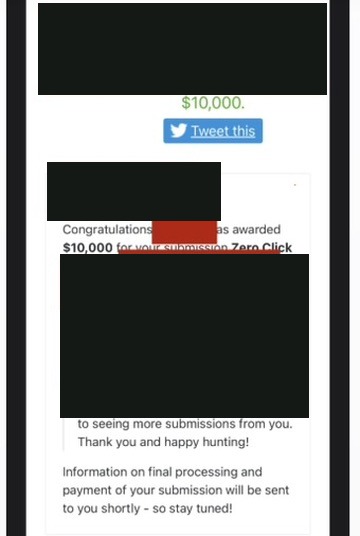
A redacted notification recognizing a zero-click report with a $10,000 award and describing payment processing as a later step.

Read write-up & view evidence

Public record

The screenshot contains an award message stating $10,000 and a congratulations message for the zero-click submission. Identifying content is redacted. The remaining correspondence mentions that further information about final processing and payment will follow.

Technical details

The target, affected component, discovery workflow, reproduction steps, and technical impact are redacted due to NDA. This public record intentionally does not reconstruct the hidden report from fragments of the notification.

Award versus payment

An award notification and a completed payment are different records. This entry describes the former; the screenshot alone does not establish that funds were received or when payment completed.

Relationship to other reports

This notification is presented separately as an evidence item. It has not been matched to the other report screenshots, and the site does not add the award amounts into a lifetime earnings total or claim that every screenshot is a separate paid bounty.

Screenshot evidence

The visible award amount is $10,000. Recipient, program, and report details are obscured.
The visible award amount is $10,000. Recipient, program, and report details are obscured. Open full image ↗
03 / REPORT RECORDREDACTED DUE TO NDA

Object authorization · unauthorized editing

Critical label shown

A report-list entry describing unauthorized editing of another user’s records through an object identifier.

Read write-up & view evidence

Reported issue

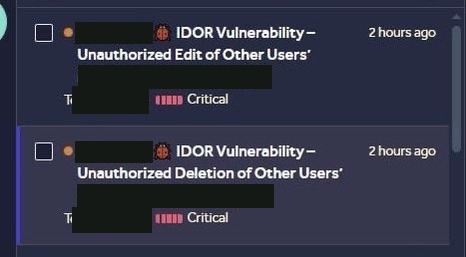
The visible report title describes an insecure direct object reference (IDOR) involving unauthorized editing of another user’s records. The security property at issue is whether one account can modify an object that belongs to another account.

Evidence and scope

The screenshot shows an edit report and a separate deletion report, each with a Critical label. This entry covers the editing report only. The screenshot is a report-list view, not a reproduction transcript or a confirmation of program acceptance.

Potential impact described by the report

Unauthorized modification would affect the integrity of another account’s data. The public evidence does not establish the number of affected users, the fields that could be changed, the prerequisites, or whether the Critical label was assigned or accepted by the program.

NDA redactions and outcome

The program, recipient, report identifier, object parameter, endpoint, requests, and proof-of-concept details are withheld. No award, remediation confirmation, or final resolution is visible in this evidence; those outcomes are not claimed.

Screenshot evidence

Shared evidence for two separate report-list entries: unauthorized editing and unauthorized deletion. Report IDs, recipient, and parameter name are obscured.
Shared evidence for two separate report-list entries: unauthorized editing and unauthorized deletion. Report IDs, recipient, and parameter name are obscured. Open full image ↗
04 / REPORT RECORDREDACTED DUE TO NDA

Object authorization · unauthorized deletion

Critical label shown

A separate report-list entry describing unauthorized deletion of another user’s records.

Read write-up & view evidence

Reported issue

The lower entry in the supplied screenshot describes an IDOR report involving unauthorized deletion of another user’s records. This concerns the authorization boundary around a destructive operation, rather than the editing operation described in the adjacent report.

Why it is a separate write-up

The screenshot displays two distinct report IDs and two different operation types. The editing and deletion entries are therefore documented separately, while sharing the same evidence image. They are not counted as two paid awards.

Potential impact described by the report

A cross-account deletion flaw could affect the availability and integrity of another user’s records. The screenshot does not establish recoverability, affected population, required access, or whether this behavior was independently reproduced during triage.

Status and disclosure

A Critical label is visible, but acceptance, resolution, and bounty payment are not shown. The program, report ID, object parameter, endpoint, and reproduction details are redacted due to NDA. No destructive test procedure is published.

Screenshot evidence

The lower entry is the deletion report. It shares a screenshot with the related edit report but has its own redacted report ID.
The lower entry is the deletion report. It shares a screenshot with the related edit report but has its own redacted report ID. Open full image ↗
05 / TRIAGE UPDATESREDACTED DUE TO NDA

Reflected XSS · classification and priority review

P3 → P5 shown

Two notifications for the same reflected XSS report, combined into one record of its classification and priority changes.

Read write-up & view evidence

Reported issue

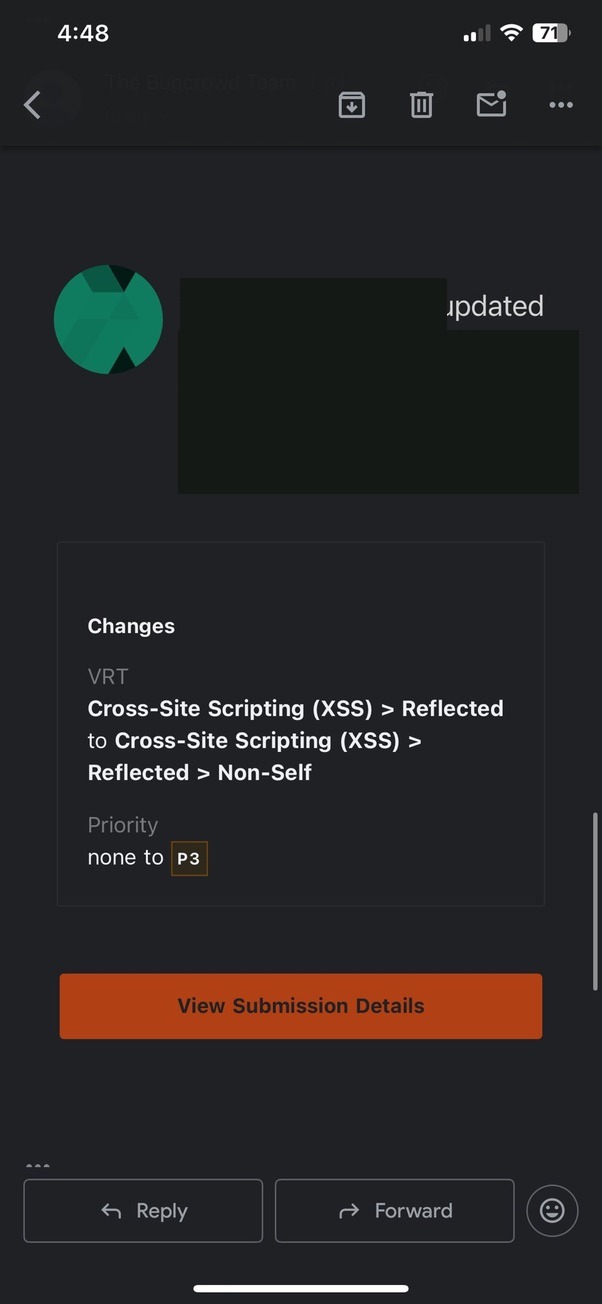
The original notification titles identify the same reflected cross-site scripting report. The target-specific title and parameter details are withheld in this public version. The visible classification change describes reflected, non-self XSS.

Triage history

One notification changes the classification from reflected XSS to reflected, non-self XSS and changes priority from none to P3. The other changes priority from P3 to P5. These are updates to one report, not two independent findings.

Interpreting the result

The public record includes both updates rather than presenting only the higher priority. The latest priority transition shown is P3 to P5. The screenshots do not explain the reviewer’s reasoning, establish the current live status, or show an award.

NDA redactions

Program and product identifiers, reviewer identity, the affected input, URL, payload, browser behavior, and reproduction steps are withheld. The screenshots demonstrate the review history; they do not serve as a public exploit demonstration or proof of remediation.

Screenshot evidence

Classification update to Reflected → Non-Self, with priority changing from none to P3. Target and reviewer identity are obscured.
Classification update to Reflected → Non-Self, with priority changing from none to P3. Target and reviewer identity are obscured. Open full image ↗
A subsequent priority update shows P3 changing to P5. The target-specific title is obscured.
A subsequent priority update shows P3 changing to P5. The target-specific title is obscured. Open full image ↗
06 / REPORT RECORDREDACTED DUE TO NDA

Account takeover · triaged report

P1 · Triaged · In progress

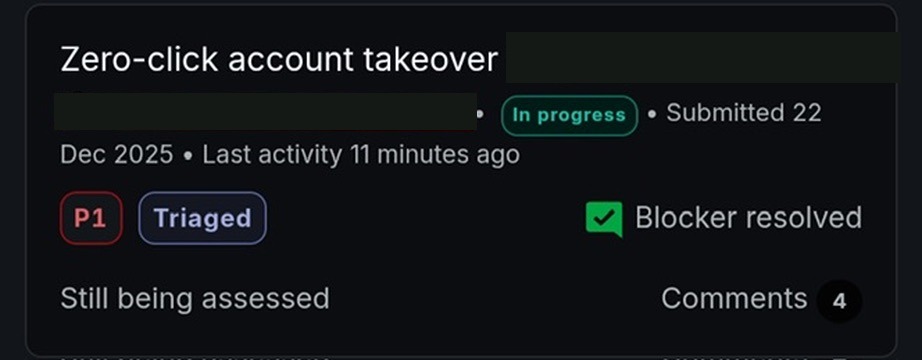
A report status screenshot showing a zero-click account-takeover title, P1 priority, and a triaged but ongoing assessment.

Read write-up & view evidence

Reported issue

The visible report title describes zero-click account takeover. The mechanism and identifying details are redacted due to NDA. The title is recorded as the report’s stated issue; the public screenshot does not contain the technical demonstration.

Assessment shown

The screenshot shows a submission date of 22 December 2025, P1 priority, Triaged status, and In progress. It also says Still being assessed. These labels describe the captured record and are not represented as a live status feed.

Meaning of the blocker update

The green Blocker resolved indicator is preserved as part of the evidence. Resolving a workflow blocker does not, by itself, establish that the underlying vulnerability was fixed or that a bounty was awarded. No such conclusion is drawn here.

Public disclosure limit

Account identifiers, program identity, the mechanism, technical prerequisites, payloads, and reproduction sequence are withheld. The screenshot supports the report’s triage state but does not document payment, final severity acceptance, or a completed remediation.

Screenshot evidence

P1, Triaged, In progress, Still being assessed, and Blocker resolved are visible. The program and mechanism are obscured.
P1, Triaged, In progress, Still being assessed, and Blocker resolved are visible. The program and mechanism are obscured. Open full image ↗
07 / ASSESSMENT RECORDREDACTED DUE TO NDA

Business logic · high-severity assessment

CVSS 8.2 · Under review

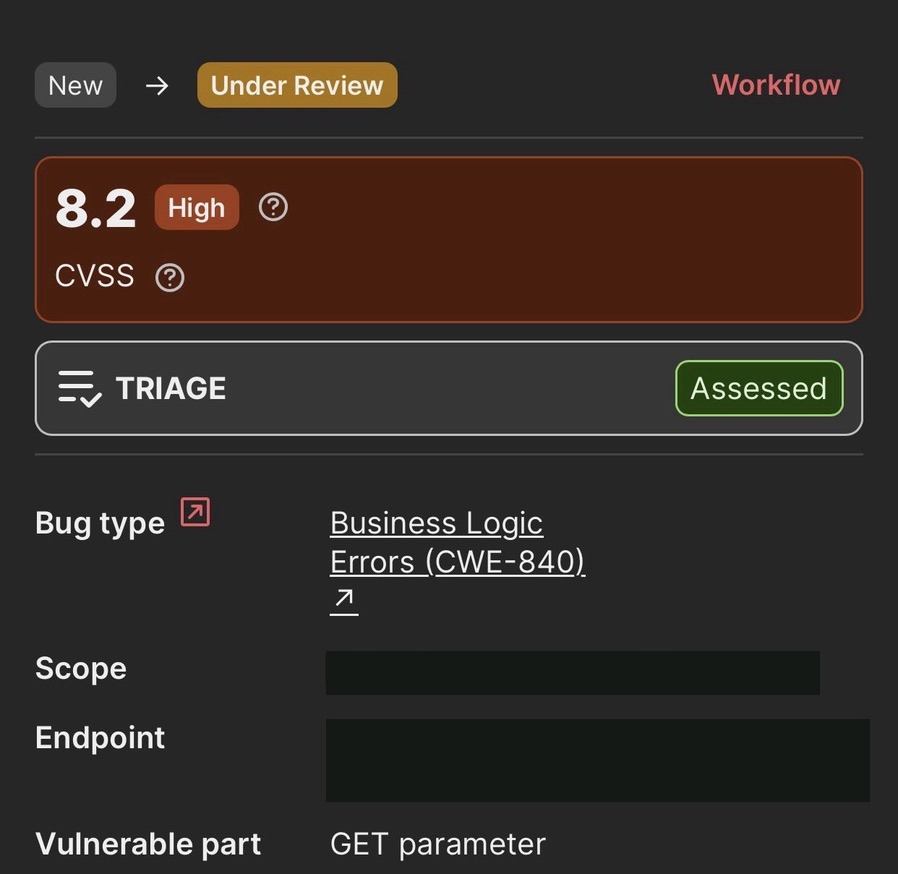
A redacted assessment showing a business-logic classification, a High score of 8.2, and an Under Review workflow state.

Read write-up & view evidence

Visible classification

The screenshot classifies the report as Business Logic Errors (CWE-840). It shows a CVSS score of 8.2 with a High label and identifies a GET parameter as the vulnerable part. The parameter name, scope, and endpoint are withheld.

Review state

The workflow shows New transitioning to Under Review, while the triage panel says Assessed. These are the states visible in the capture; they do not prove that a fix was deployed, a report was publicly disclosed, or an award was paid.

Limits of the assessment

No CVSS vector, affected business workflow, reproduction sequence, or impact narrative is included in the supplied image. This write-up therefore does not infer specific privileges, financial loss, account access, or exploit conditions from the numerical score alone.

NDA redactions

The target domain, endpoint, request parameters, sensitive data, and technical proof are redacted due to NDA. The public evidence is an assessment summary, not a complete technical report. No final resolution or bounty amount is visible.

Screenshot evidence

CVSS 8.2 High, Assessed triage, Business Logic Errors (CWE-840), and Under Review are visible. Scope and endpoint are obscured.
CVSS 8.2 High, Assessed triage, Business Logic Errors (CWE-840), and Under Review are visible. Scope and endpoint are obscured. Open full image ↗
08 / RELATED SUBMISSIONSREDACTED DUE TO NDA

Azure App Service · subdomain takeover submissions

P3 · New · In progress

Two similar subdomain-takeover submissions grouped into one write-up because their redacted assets cannot be distinguished publicly.

Read write-up & view evidence

Reported issue

Both visible titles describe subdomain takeover on Azure App Service. The affected hostnames and program identities are redacted. The image does not include DNS records, a service response, an asset claim, or proof of control.

Grouping the evidence

The screenshot contains two similar submissions dated 18 October 2025. Because the identifying content is obscured, it is not possible to establish from this image whether they affect different assets or overlap. They are grouped rather than counted as two distinct confirmed vulnerabilities.

Assessment state

Both entries show P3 and New, with In progress and Still being assessed indicators. These labels record the submission state at capture time. They do not establish program validation, completed remediation, or a bounty award.

Disclosure boundary

Target domains, DNS configuration, resource identifiers, verification details, and reproduction instructions are redacted due to NDA. No live asset is identified and no takeover instructions are published in this portfolio entry.

Screenshot evidence

Two Azure App Service subdomain-takeover entries, each showing P3, New, and Still being assessed. Target identities are already redacted.
Two Azure App Service subdomain-takeover entries, each showing P3, New, and Still being assessed. Target identities are already redacted. Open full image ↗

Let’s talk security.

For professional opportunities and conversations about responsible security research.

Contact me